Experiencing a breach? Contact us
turingtower

VIGIL

Continuous security validation for regulated enterprises

Discover exposures, validate weaknesses and generate executive-ready reports across your external attack surface.

Talk to an expert

Annual pentests are no longer enough

Modern environments change constantly. Continuous validation helps identify exploitable exposure before attackers do.

Core Pillars

From exposure to proof

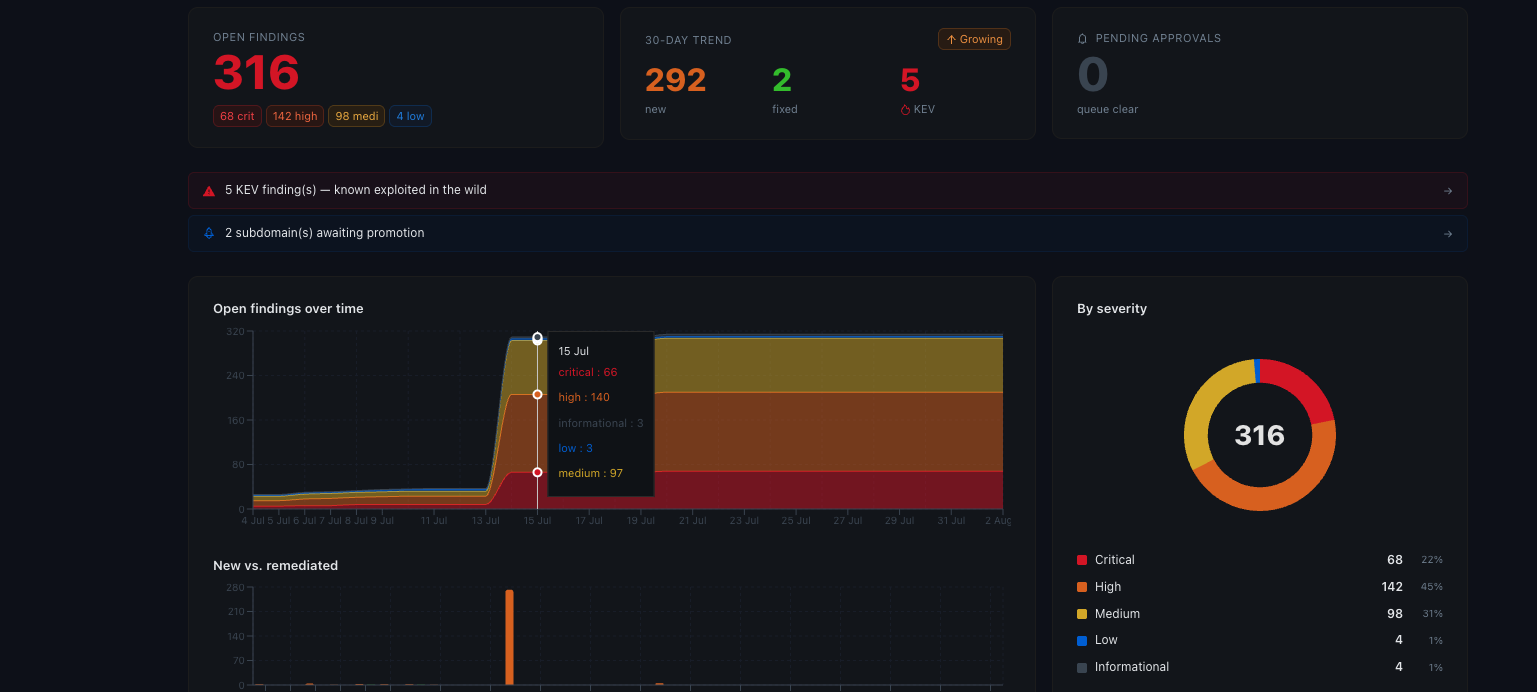
VIGIL dashboard showing 316 open findings by severity, a 30-day trend of new versus fixed issues with a KEV count, an open-findings-over-time area chart, and a severity breakdown donut

Open exposure, trended over time

Findings are broken out by severity and tracked as they open and close, with known-exploited (KEV) issues flagged as soon as they appear. Because scanning runs continuously, the view reflects the estate as it is now, not as it stood at the last assessment.
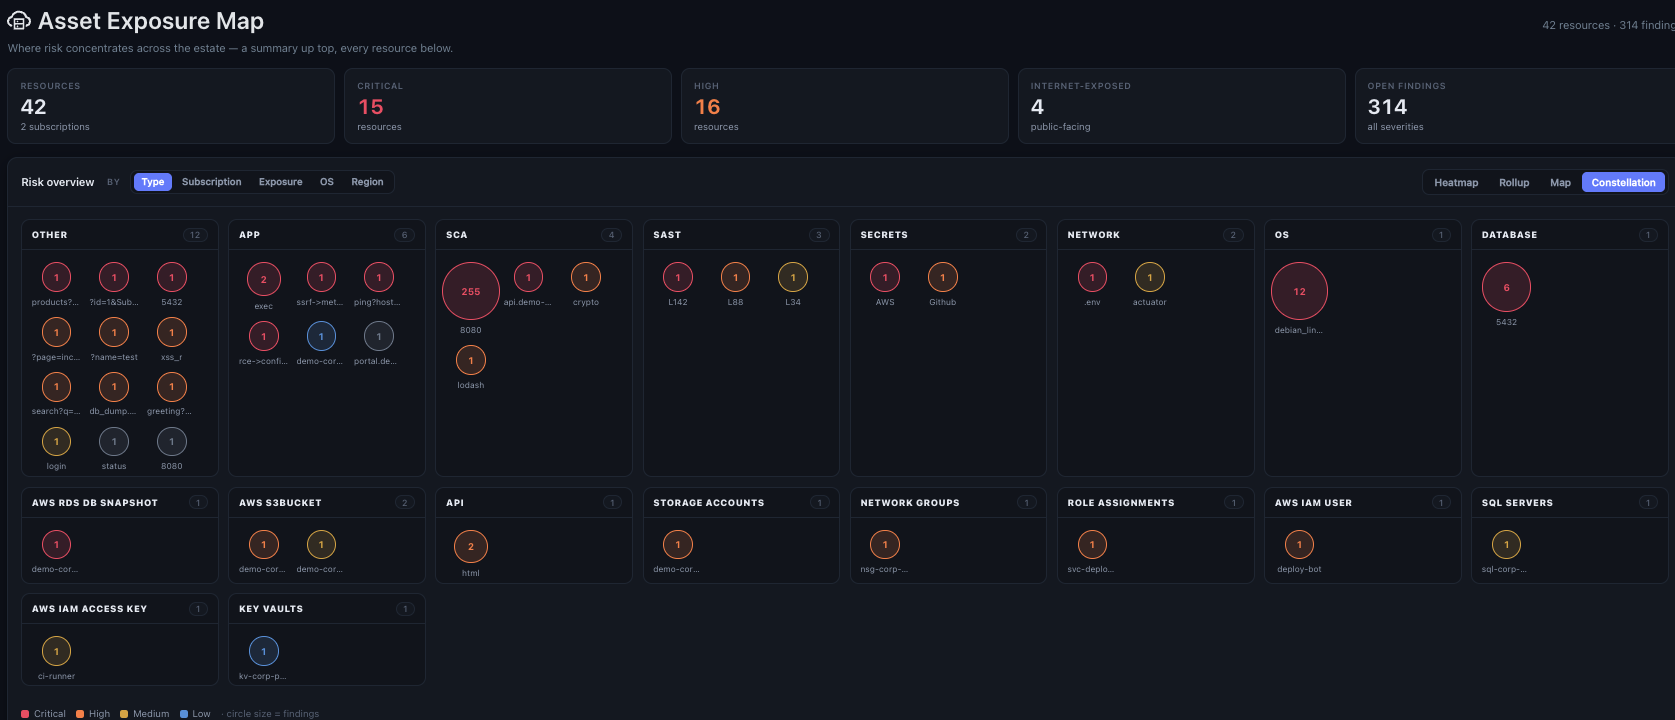
VIGIL asset exposure map showing 42 resources with critical, high, and internet-exposed counts, and a constellation of asset groups such as apps, cloud storage, secrets, databases, and identities sized and colored by finding severity

The whole external estate, mapped

Every domain, API, cloud resource, and identity VIGIL can reach is laid out by type and severity, with the internet-facing assets called out and a finding count on each. A public database snapshot or an open storage bucket shows up here as its own node.

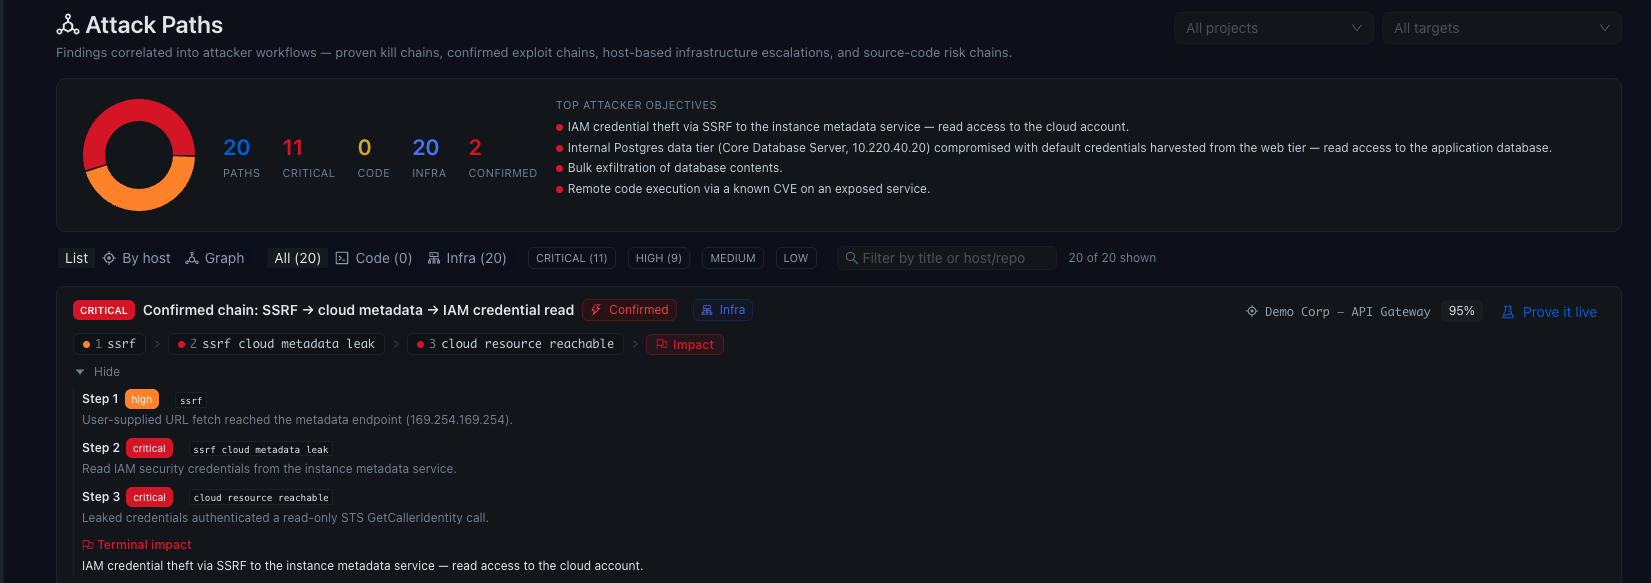
VIGIL attack paths view summarizing 20 correlated paths with 11 critical and 2 confirmed, listing top attacker objectives, and expanding a confirmed SSRF to cloud-metadata to IAM-credential chain with three evidenced steps and a 'prove it live' control

Exploitable, and proven

VIGIL correlates findings into full attack chains and confirms the ones that actually work. This SSRF path is traced step by step to stolen cloud credentials, each step carrying its own evidence and marked confirmed at 95%. Triage then starts from what an attacker can reach, not a severity score read in isolation.

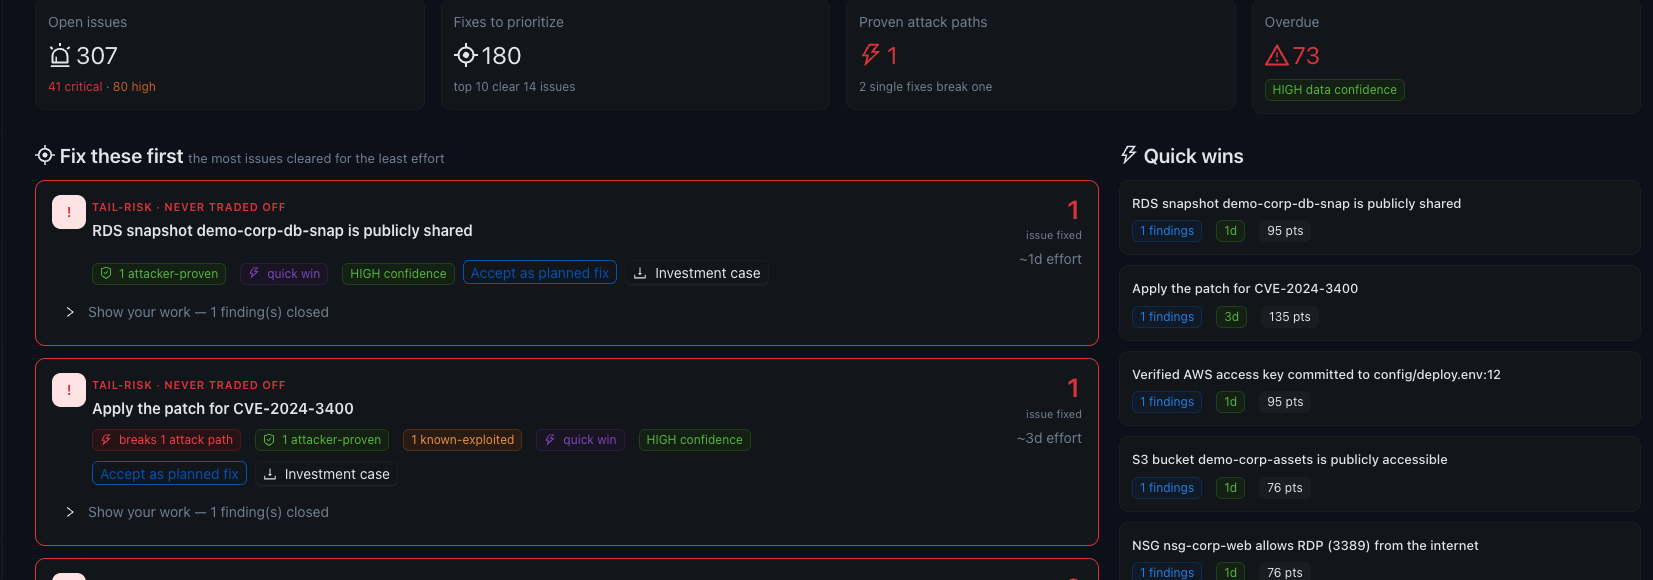
VIGIL Compass view with KPIs for open issues, fixes to prioritize, proven attack paths, and overdue items, above a 'fix these first' list of ranked remediations tagged with effort and confidence, and a quick-wins column

Fix what clears the most, first

The same findings are ranked by the exposure they close against the effort they take. A short list rises to the top, the fixes that break a proven attack path are flagged, and the quick wins are separated out with their effort in days.

Three steps to continuous validation

step i

Enumerate

Map domains, subdomains, services, APIs, and infrastructure exposure continuously.

step ii

Validate

Run AI-assisted validation with approval-gated offensive workflows and replayable evidence.

step iii

Report

Generate audit-ready findings, exposure narratives, and executive reports automatically.

Insurance Use Cases

VIGIL continuously discovers, validates, and reports on external exposures across your evolving environment.

Stay ahead of evolving threats