Experiencing a breach? Contact us
turingtower

AURORA

Modern Cyber GRC built for regulated environments

Centralize governance, risk, compliance, and third-party oversight in one operational platform.

Get started

Complex regulations, operational clarity

Regulatory requirements, third-party risk, and control gaps evolve constantly. AURORA keeps compliance, governance, and cyber risk continuously measurable and audit-ready.

Core Workflow

Cyber risk, measured and audit-ready

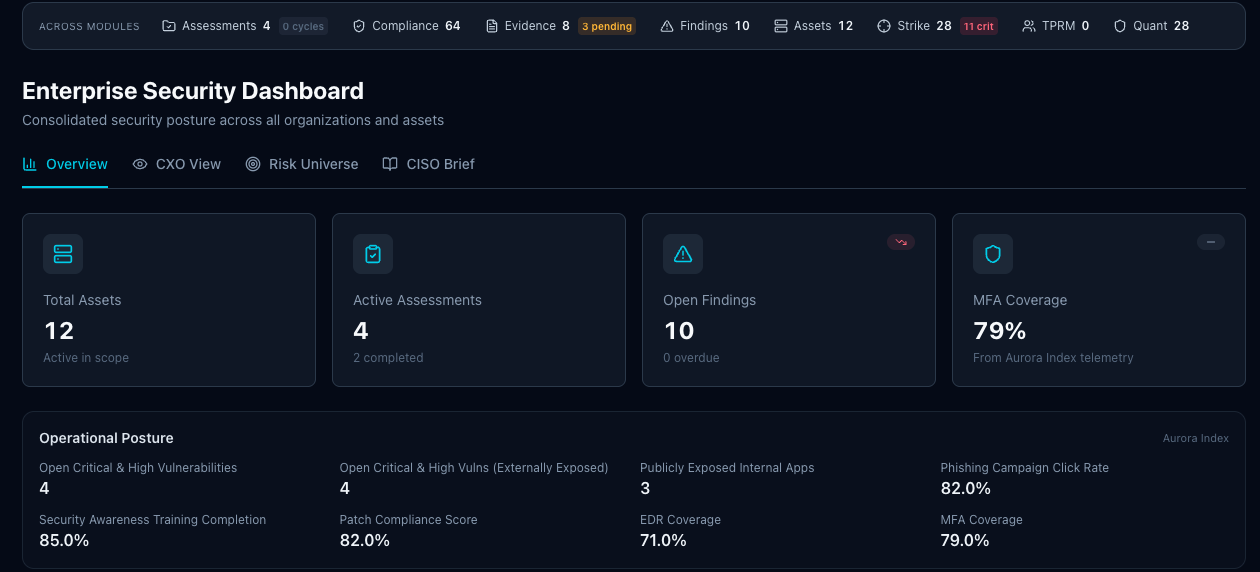
AURORA enterprise security dashboard with a cross-module summary bar, KPI tiles for assets, assessments, open findings and MFA coverage, and an operational posture panel showing patch compliance, EDR coverage, and phishing click-rate metrics

One posture across every module

Assessments, findings, evidence, assets, and third-party risk report into a single view. The operational metrics that drive it sit directly beneath, including patch compliance, EDR and MFA coverage, and phishing click rate, each read from live data rather than a quarterly spreadsheet.
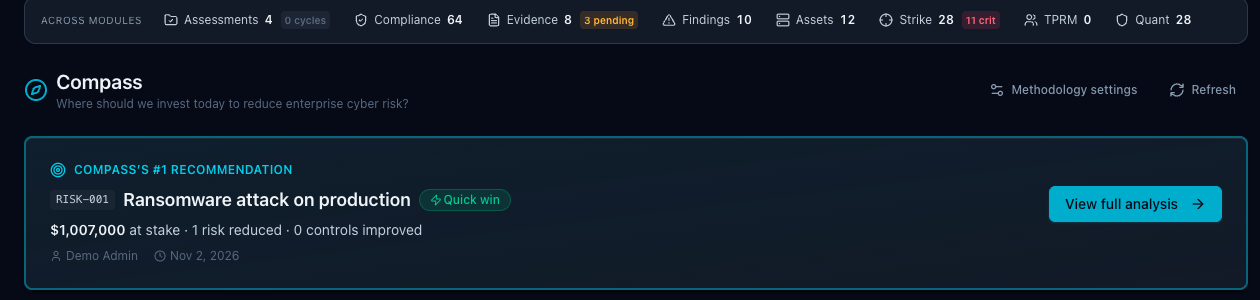
AURORA Compass view headed 'where should we invest today to reduce enterprise cyber risk', showing a top-ranked recommendation to address a ransomware risk with the dollar amount at stake and a quick-win tag

Where to reduce the most risk next

Compass ranks the available actions by how much exposure each one removes, and its top recommendation names the risk, the amount at stake, and the effort to close it. Remediation budget goes to the work that lowers risk the most.

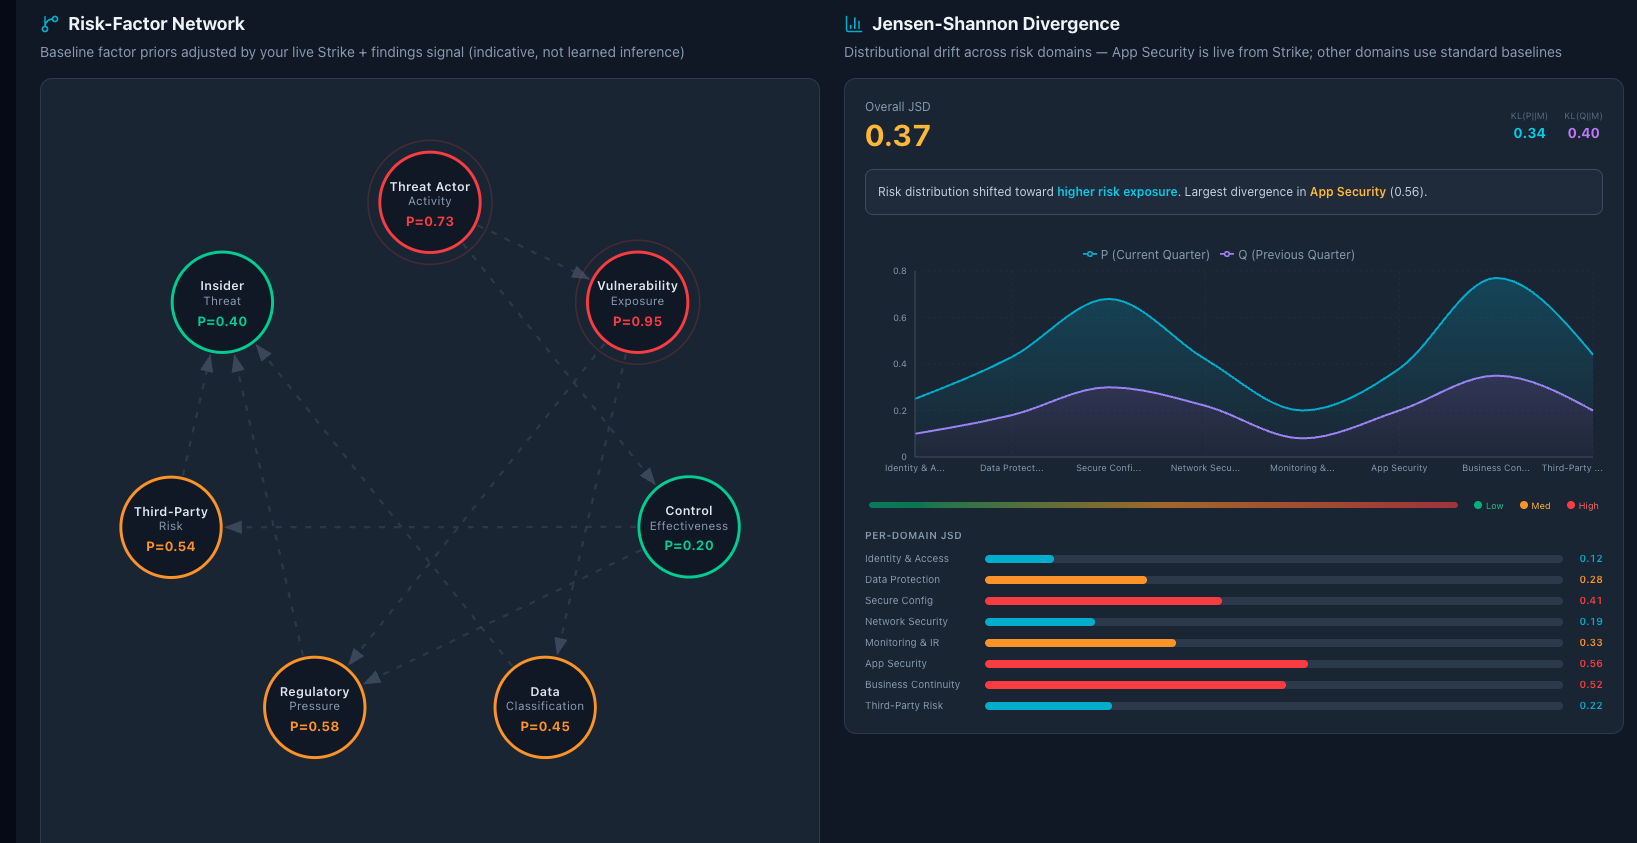
AURORA Quant view with a risk-factor network of probability-scored nodes such as threat actor activity and vulnerability exposure, beside a Jensen-Shannon divergence panel showing distributional drift across risk domains

Risk quantified, not asserted

Aurora Quant models each risk factor as a probability adjusted by your live findings, then measures how the distribution moves quarter over quarter with Jensen-Shannon divergence. The result shows which domains are drifting toward higher exposure and by how much.

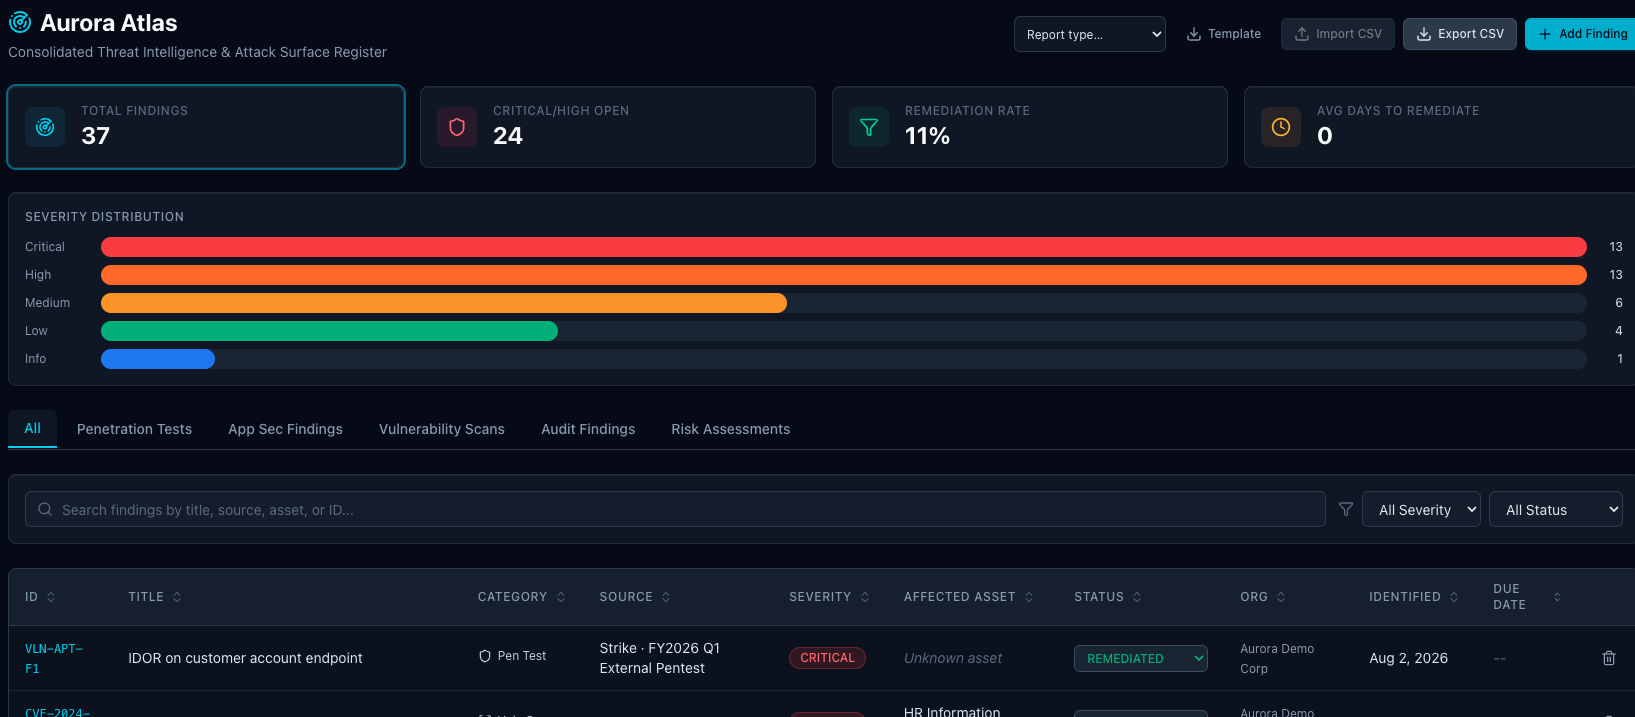
AURORA Atlas consolidated findings register showing total findings, critical and high open counts, remediation rate, a severity distribution chart, and a table of findings with category, source, severity, affected asset, and status columns

Every finding in one register

Penetration tests, vulnerability scans, and audit findings land in a single register, each carrying severity, affected asset, source, and remediation status. Remediation rate and time-to-fix stay current, and the whole register exports when a regulator asks for it.

From asset to report in three easy steps

step i

Create Assets

Add domains and IP ranges to your asset inventory, manually or via API.

step ii

Launch Scan

On-demand or scheduled scans test OWASP vectors, CVEs, and custom checks.

step iii

Review and Export

Explore your interactive dashboard, assign fixes, or export a detailed PDF or CSV report.

What sets us apart

Continuous Compliance

Operationalize regulatory obligations across teams, controls, vendors, and reporting systems.

Threat and Risk Visibility

Track vulnerabilities, incidents, KRIs, and third-party exposure from a unified risk registry.

Evidence-Driven Governance

Maintain audit-ready evidence, remediation history, and regulatory reporting in real time.

Audit-ready by design

AURORA keeps compliance, governance, and cyber risk continuously measurable and audit-ready.

Operationalize compliance before regulators demand it